Novel Malware Built to Survive the Analyst
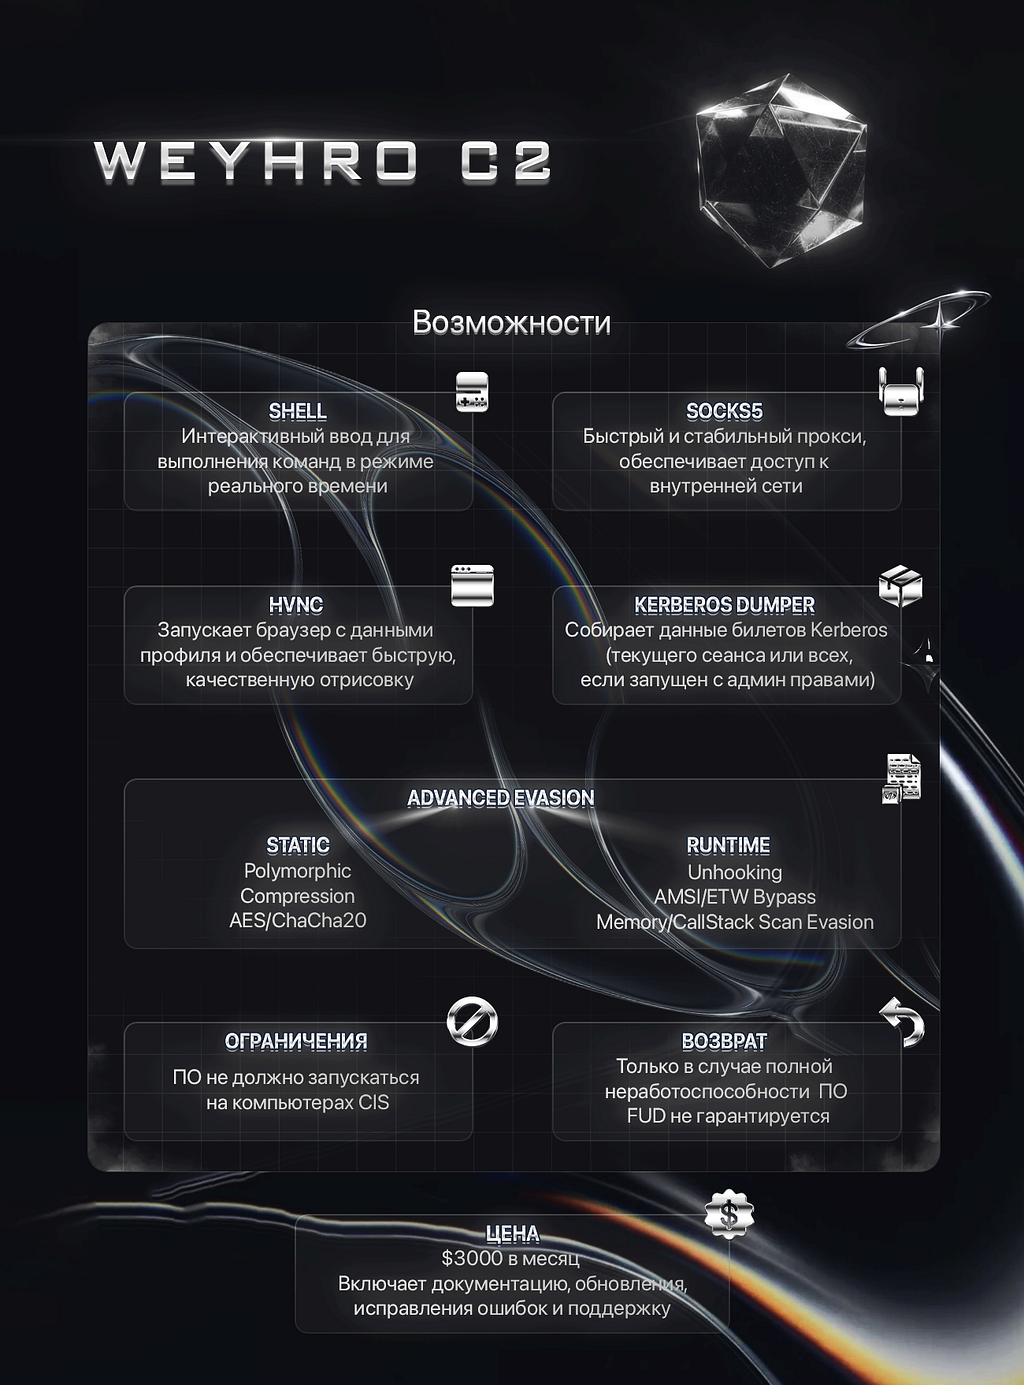
Four payloads built to resist analysis: PavokwiLoader, an 80,000-instruction monstrosity hiding its payload in operand bytes; RMMCRAT, a custom C++ "RAT"; a fake RMM agent; and an obfuscated Python loader with a brute-forced decryption key.
By Malbear Labs ·
78 min read